Isolated by default
gVisor gives each workload its own filesystem, namespace and limits.
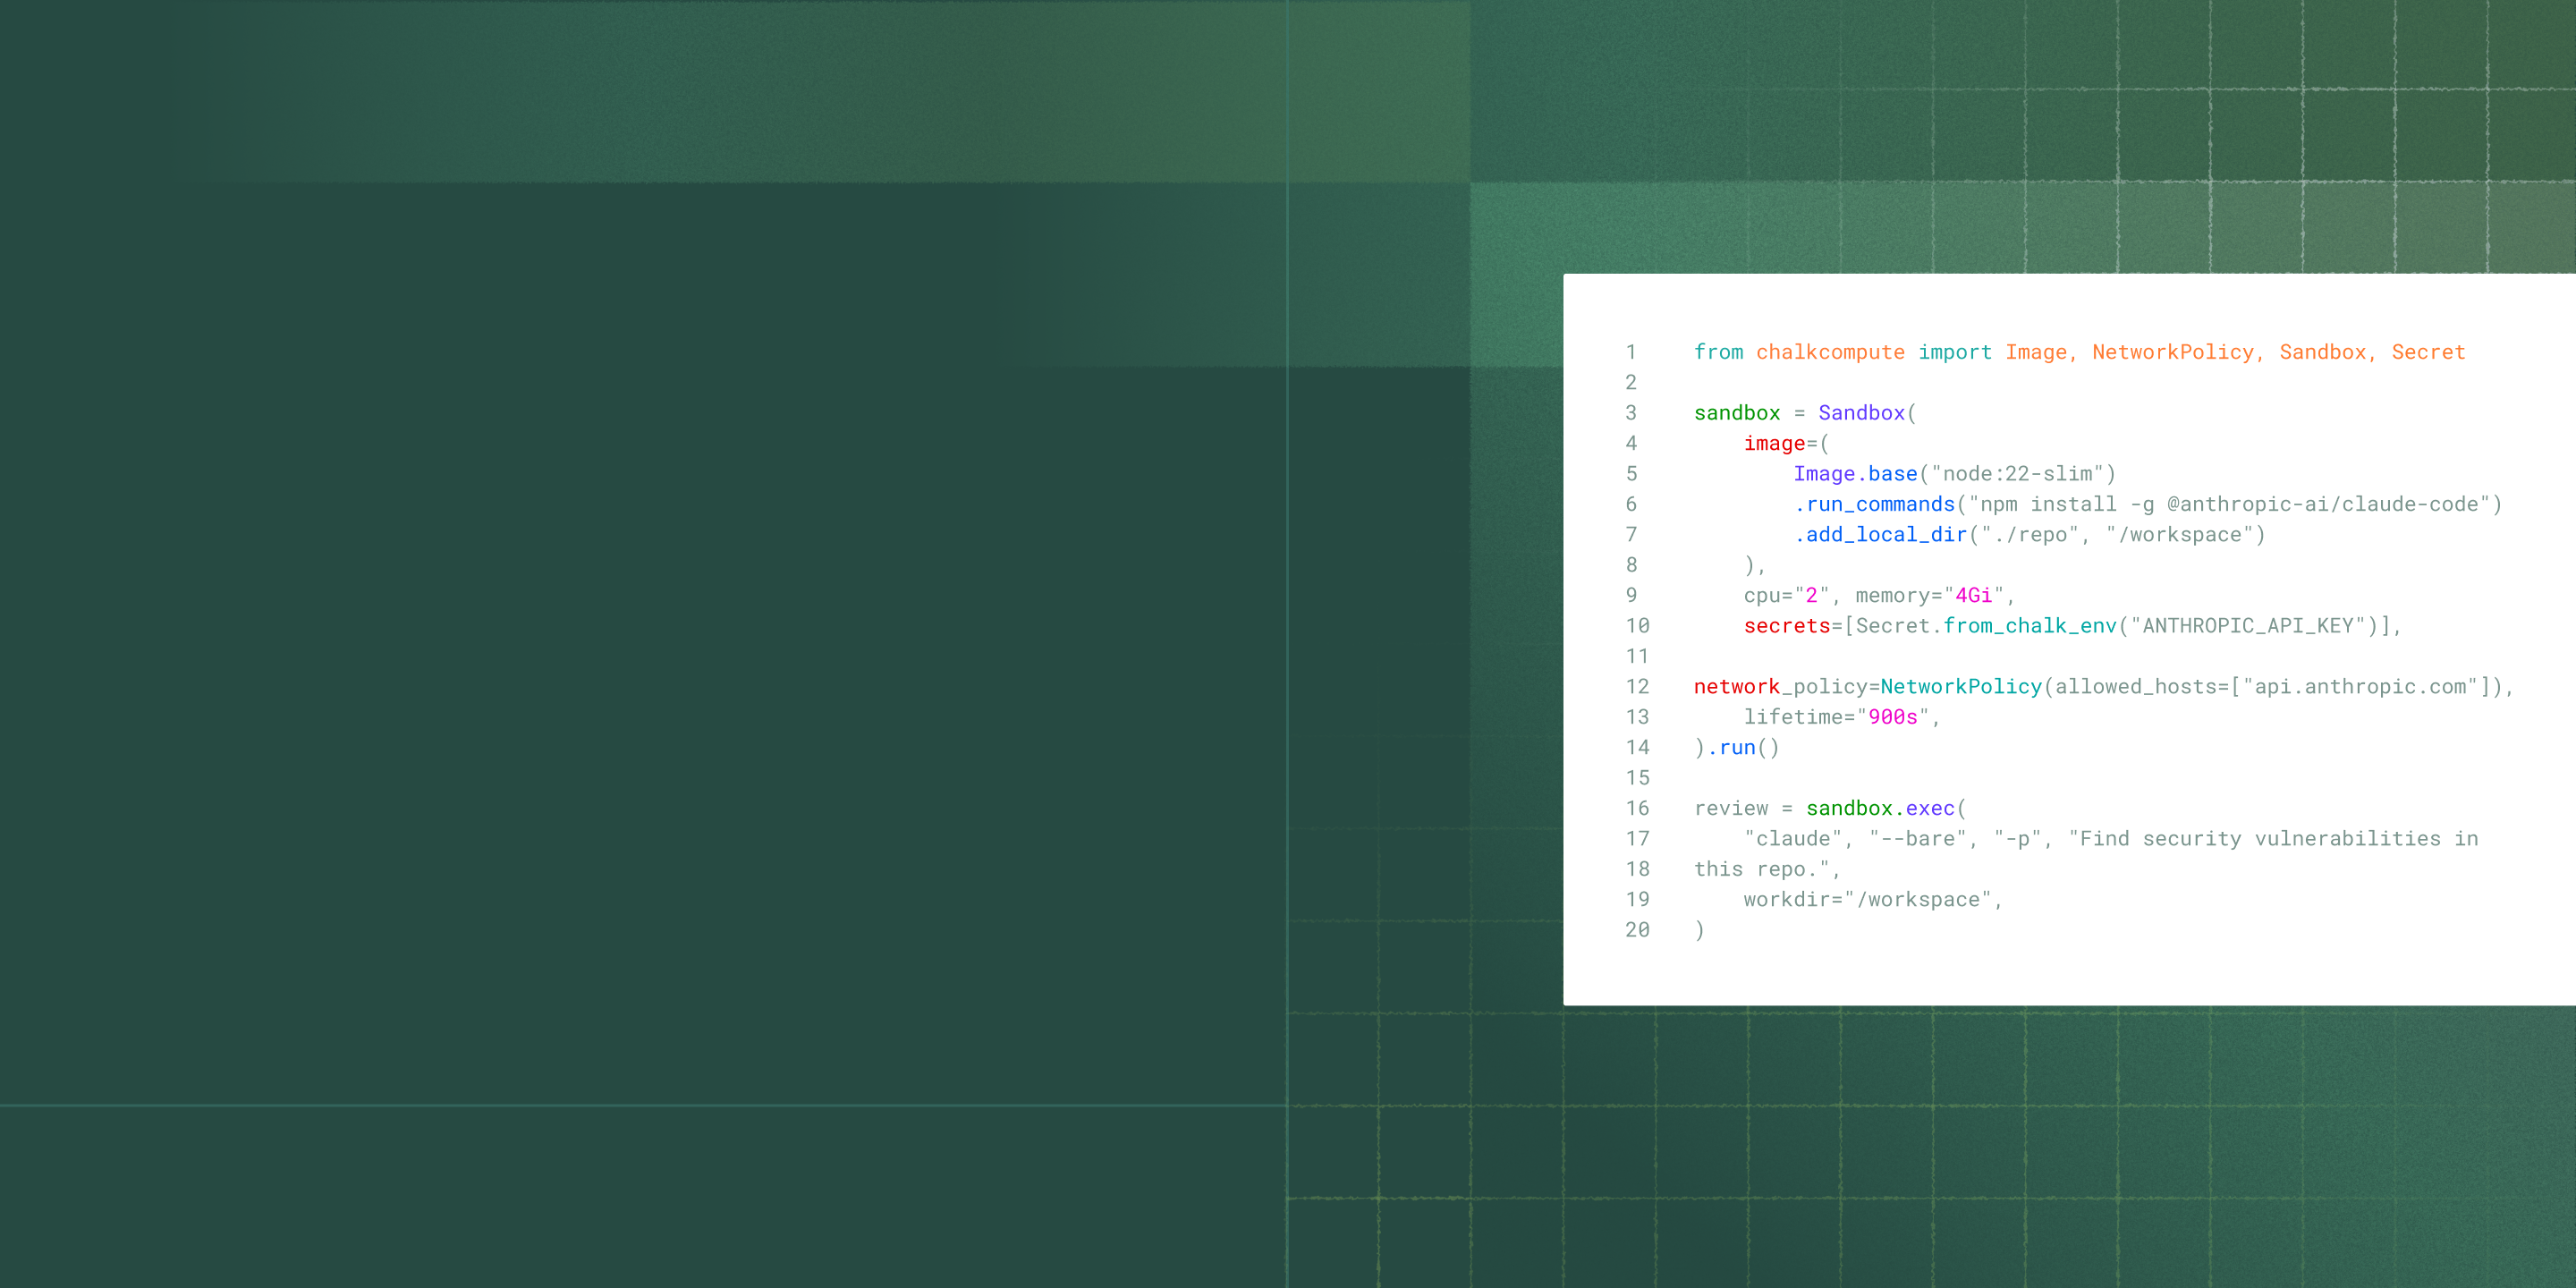
Sandbox DocsChalk runs agent-generated and untrusted code in gVisor-hardened sandboxes inside your cloud account. Your sandbox can’t talk to anything outside your network policy.
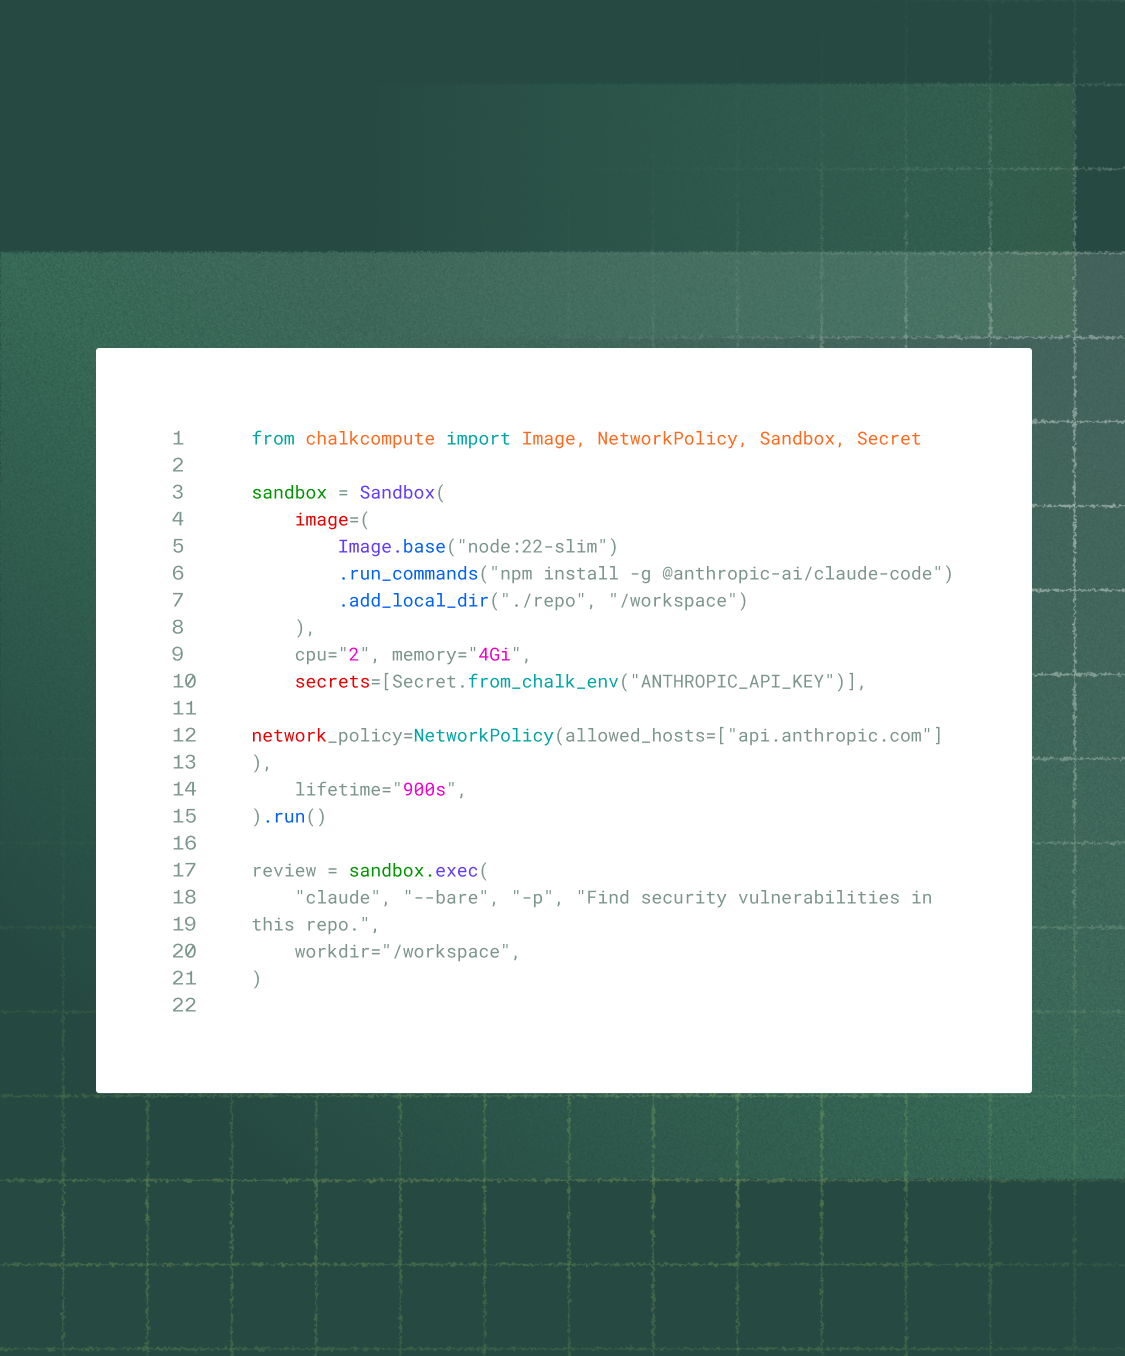




The sandbox kernel, filesystem, network, resource limits and egress are all locked down by default. Agent code never sees a shared secret.
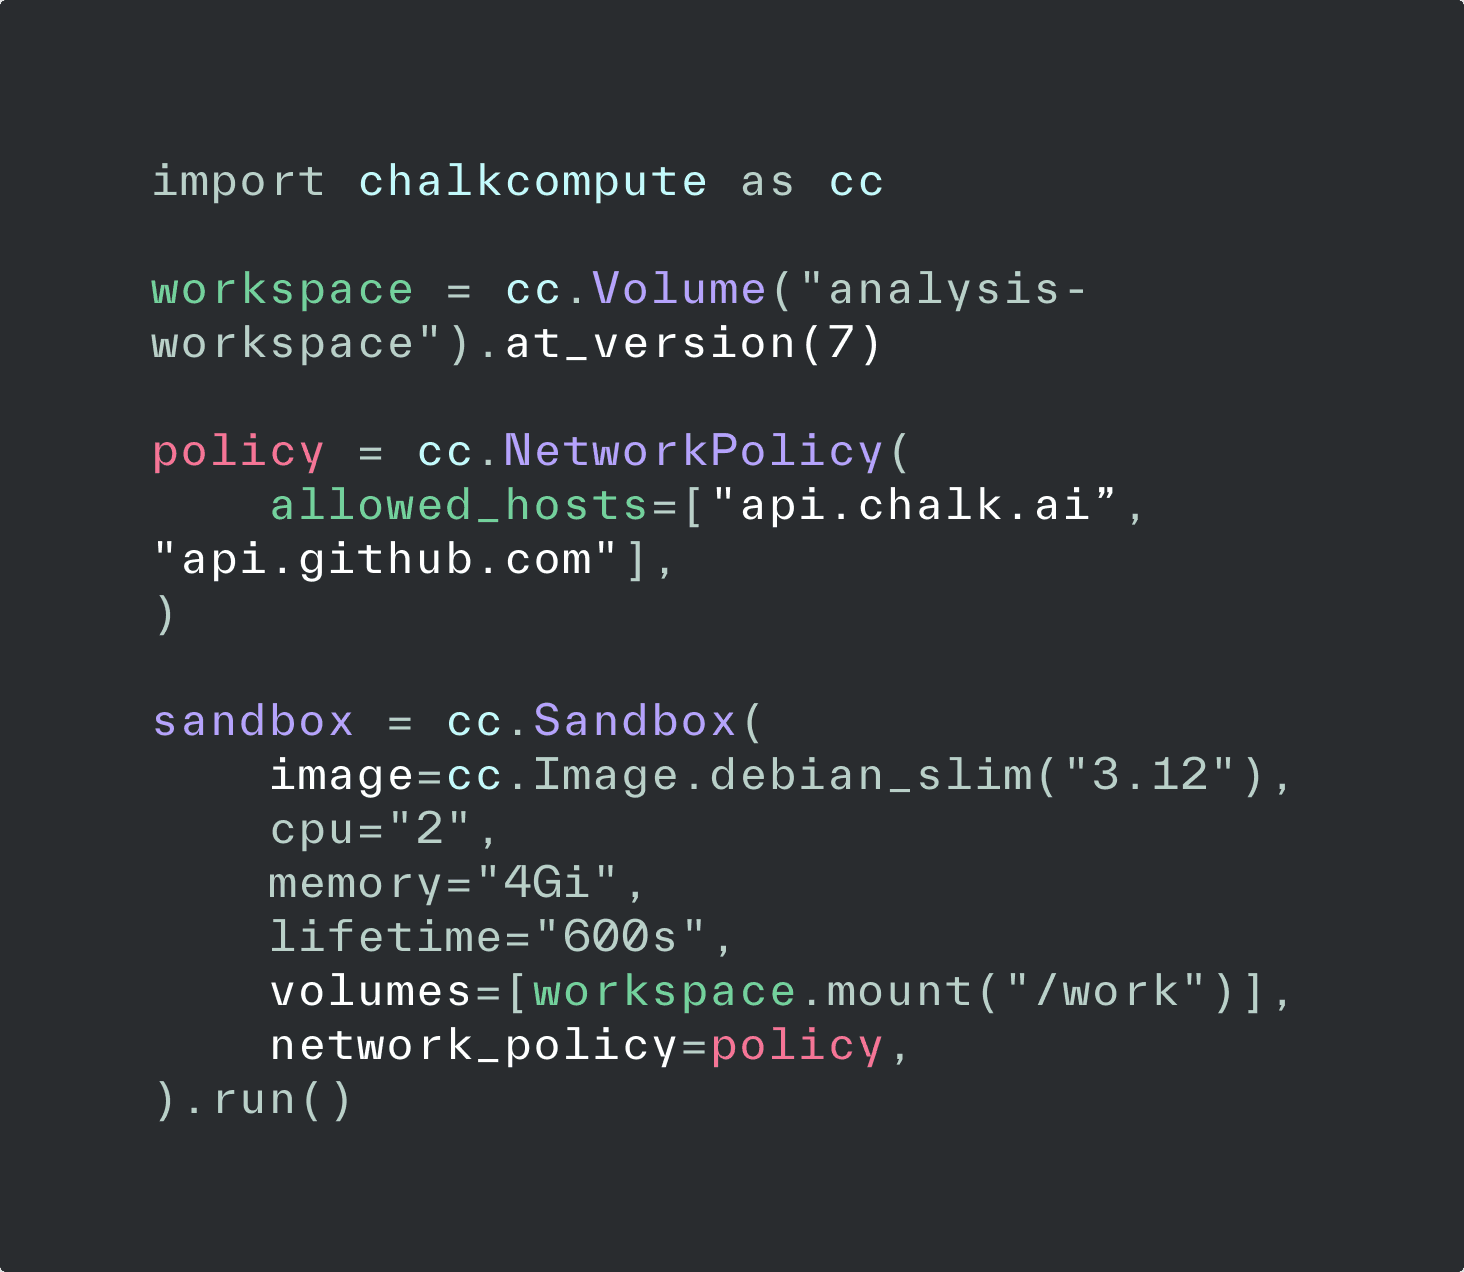
Name the hostnames, CIDRs and ports a sandbox may reach. The rest are blocked.
Even if agent code escapes the container, it can’t reach the host.
Runs in your account, on your nodes, with the CPU, memory, and GPU you set, under an IAM role or its own OIDC cloud identity.
Run a sandbox against your production data at any point in time. Every sandbox in a parallel run reads the same consistent snapshot.
Use copy-on-write versioning across sandboxes to mount the exact model, dataset, or repo you want your agent to work with.

gVisor gives each workload its own filesystem, namespace and limits.
Sandbox DocsAllowlist exact hostnames like api.github.com or wildcards like *.github.com. Anything unlisted is blocked.
Network PolicyA versioned volume for a repo, dataset or model weights.
VOLUMES & HOST POOLSSecurity signs off on agent projects. Sandboxes deploy inside the environment your security team already governs, so the second agent use case ships without opening a second review.
Security ArchitectureWhat we've been up to and where to find us next.
See why Fast Company named us on their list.
Learn how to give agents context for evals and production
How Chalk filled 40+ roles in one quarter without lowering the bar
Read more about our latest product announcement
Talk to an engineer about running agents in your own cloud.